Security operations centers (SOCs) handle large volumes of repetitive work, and there is no good reason for an analyst to perform every step by hand. Security orchestration, automation, and response (SOAR) automates repeatable work across security operations. A SOAR playbook can enrich an alert, open a ticket, pull in threat […]
SOAR can automate the response. Can it prioritize the risk?


An AI agent that can complete a complicated task is impressive. An organization that can prove the agent stayed within its authority is better prepared to put that capability to work safely. Recent investigations involving OpenAI and Anthropic show why that distinction matters. Researchers identified weaknesses in agent monitoring and […]

When AI Agents Cross the Line: Security Leaders Call for ...


Security teams already know the problems with SOAR. Playbooks take work to maintain and start to struggle when an investigation calls for context or judgment. The harder part comes when a team decides to move away from SOAR while it is still running live security workflows.  How do you replace […]

Moving Off SOAR: What Has to Happen, Step by Step


In Episode S8E10 of the Brilliance Security Magazine Podcast, host Steven Bowcut speaks with Abu Bakr Qureshi, Director of Cybercrime Disruption at Bfore, about predictive attack intelligence and the effort to stop malicious infrastructure before cybercriminals can weaponize it. Summary Traditional cyber threat intelligence relies heavily on indicators of compromise—evidence […]

Predicting and Disrupting Cybercrime Before It Strikes


Citizens routinely share highly sensitive information with government agencies, from Social Security numbers and tax records to health data and benefits applications. As cyberthreats evolve and become more sophisticated, public sector organizations face pressure to abandon outdated communication methods, such as standard email attachments and unsecured file transfers. Protecting sensitive […]

How Secure Messaging Protects Sensitive Citizen Data


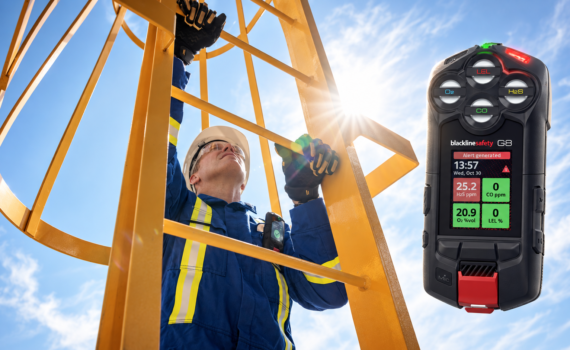
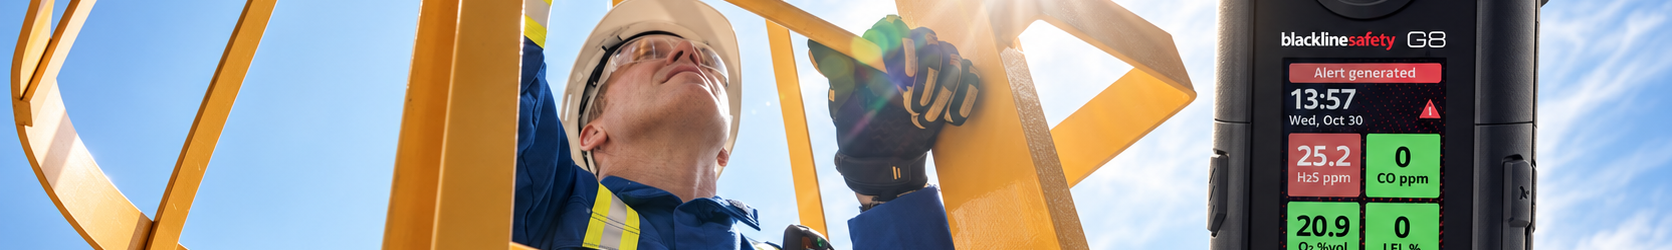
Connected safety leader to showcase G8’s expanded communications, gas detection, and worksite visibility at booth #2213 at NSC 2026 Calgary, Canada, September 14, 2026  — Blackline Safety, a global leader in connected safety technology, will feature its new G8 connected safety wearable at the 2026 National Safety Council (NSC) Safety […]

Blackline Safety’s New G8 Wearable Gains Global Traction Ahead of ...


As remote and hybrid work become more common, many organizations adopt bring-your-own-device (BYOD) programs to give employees greater flexibility while supporting productivity. A well-designed BYOD policy helps establish clear expectations around device use, data protection and access controls.  However, failing to address key details during the policy creation process can […]

5 Pitfalls to Avoid When Writing a BYOD Policy


As AI systems gain the ability to exploit vulnerabilities and follow attack paths, human oversight must remain more than a ceremonial checkpoint. There is a meaningful difference between asking artificial intelligence to identify a vulnerability and authorizing it to exploit one. The first is an extension of what automated security […]

The Guardrails That Make Autonomous Pentesting Safe


By Sam Lyne A paper record is often least supervised at the point an organisation believes it has finished with it. While active, it usually has a home and an owner. An employee file sits with HR, an invoice moves through finance and a customer form belongs to a defined […]

Data Protection: What Happens After a Paper Record Leaves the ...


While healthcare consolidation in New Jersey aims to streamline operations and reduce costs, it unintentionally creates massive, interconnected targets for cybercriminals. As hospital systems merge and share IT infrastructure, addressing unique cybersecurity vulnerabilities created by unification becomes critical. These larger networks bring exponentially larger attack surfaces and compounding security risks. […]

Addressing Unique Cybersecurity Vulnerabilities Created by New Jersey Healthcare Consolidation


Agentic AI may help security teams identify which weaknesses attackers could actually exploit—but continuous offensive testing requires evidence, boundaries, and human oversight. Security teams seldom suffer from a shortage of findings. The more constant problem is determining which findings describe a genuine path to compromise—and which will consume remediation time […]

From Vulnerability Counts to Proven Attack Paths